Primary
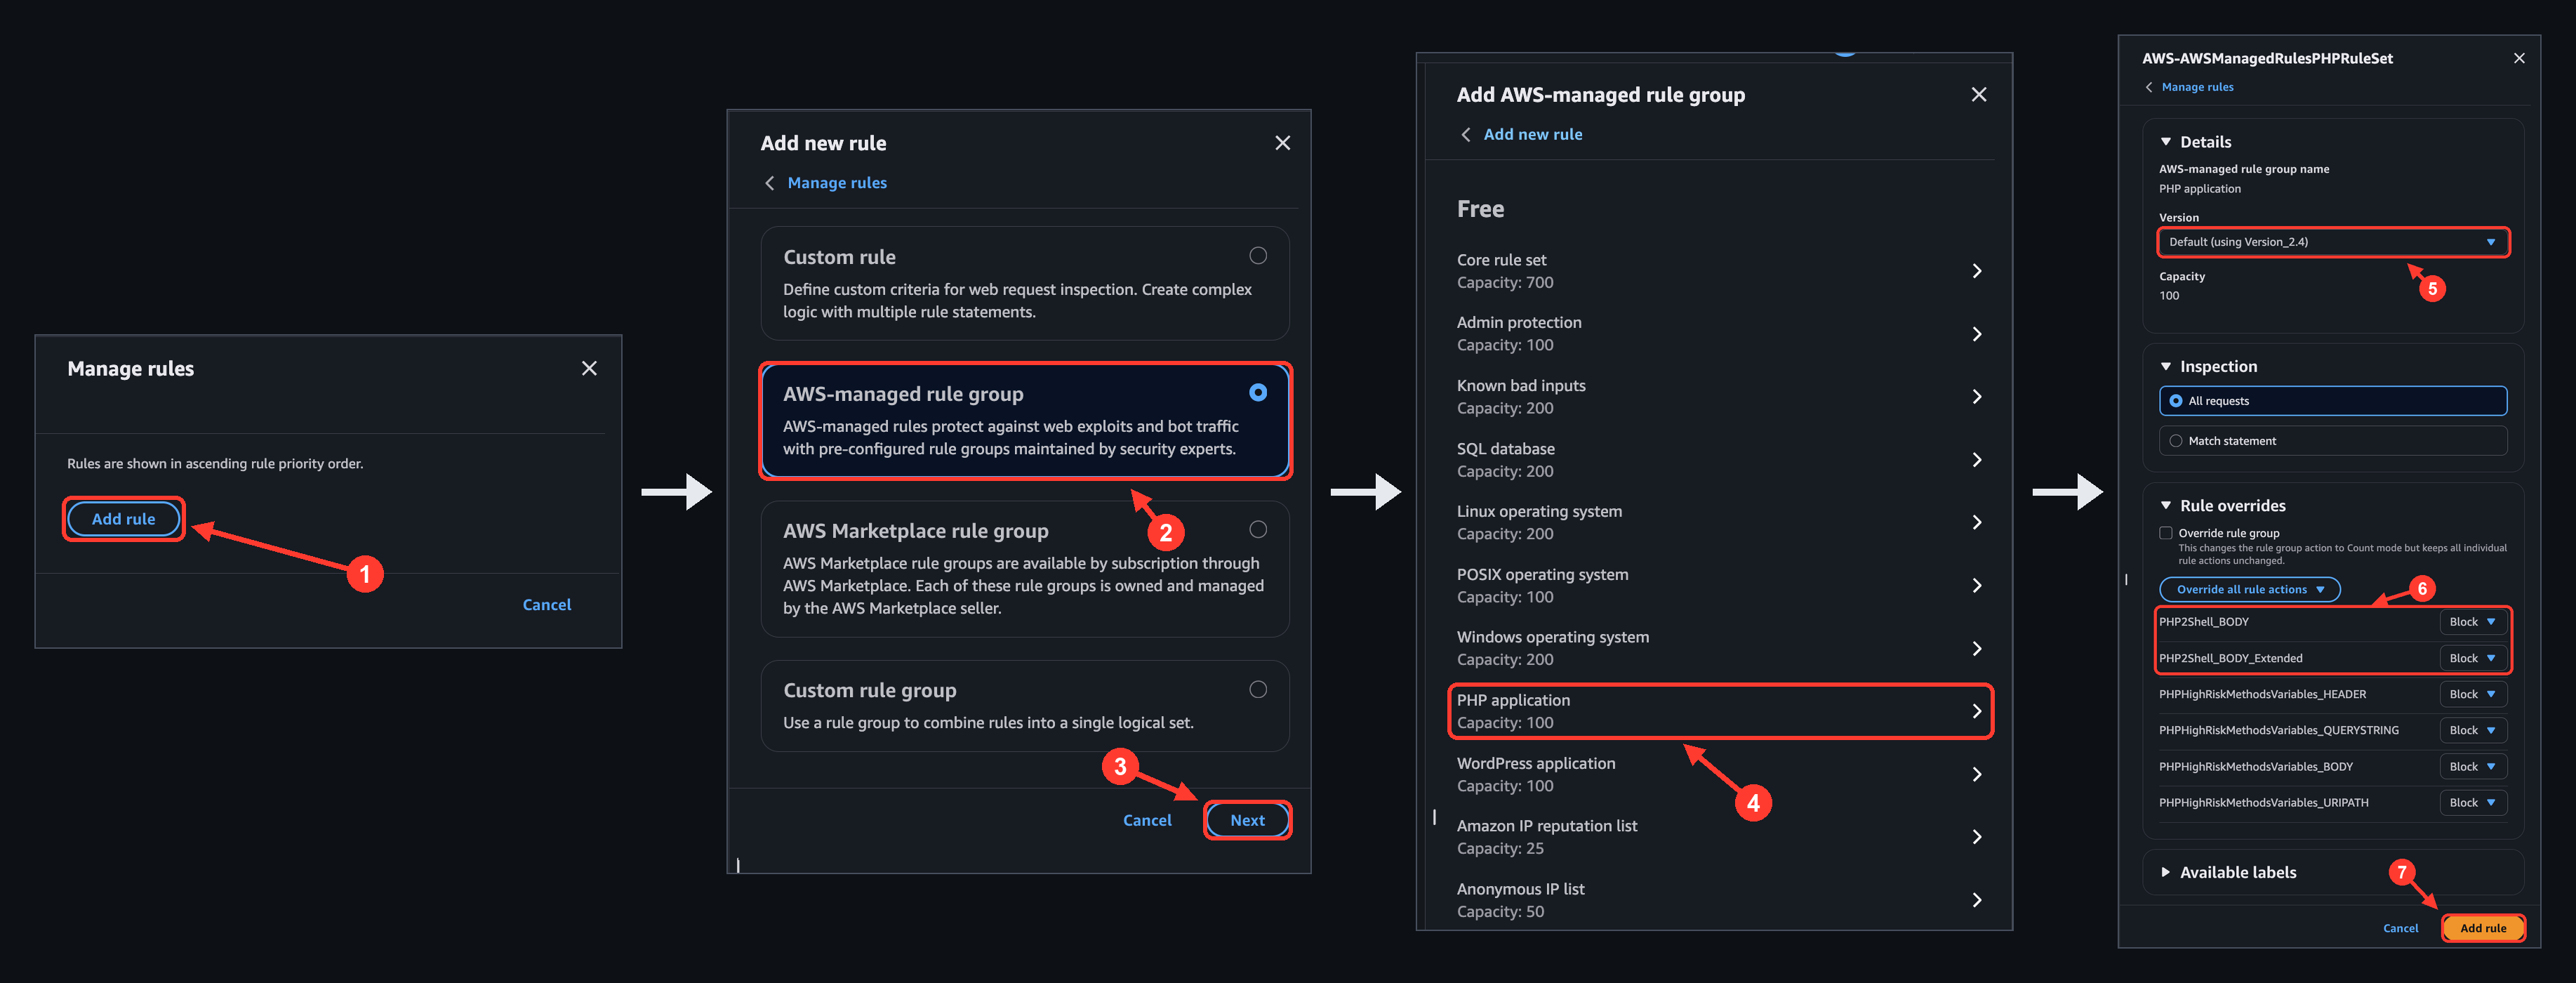
Using AWS WAF to apply mitigations for PHP2Shell RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619)
Primary source. Published by the vendor, CERT, regulator, government agency or researcher responsible.
October 29, 2026: We added guidance for end-of-life PHP versions (8.1 and earlier), including the source backports that the PHP security team published for PHP 7.4, 8.0, and 8.1. October 23, 2026 (update 2): The PHP project disclosed CVE-2026-115560, a separate remote code execution issue that the October 21 releases don’t fix. It affects only
Read the full story at AWS Security Blog ↗HackerNews24 shows a short summary only. The full article, its copyright and any corrections belong to the original publisher.
Vulnerabilities mentioned
| CVE | Severity | KEV | Description |
|---|---|---|---|
| CVE-2026-109618 | Critical 9.2 | Exploited | PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request. Some contexts may not properly account for… |
| CVE-2026-109619 | Critical 9.2 | Exploited | PHP has various global state that temporarily points into request memory. In some scenarios, global state may not be correctly reset, or may be repopulated… |
| CVE-2026-115560 | Critical 9.2 | — | Session serializer mismatch can lead to remote code execution. Session upload progress, when enabled, can store attacker-controlled data in a session key using… |
CVSS measures technical severity. Real-world risk also depends on exploitation, exposure and business impact.
Coverage from other sources (10)
- Rapid Response: php2shell, Leaked Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)
- Critical security issue affecting PHP
- CVE-2026-109618 and CVE-2026-109619: Critical Unauthenticated Remote Code Execution in PHP
- Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot
- SANS Stormcast Thursday, October 22nd, 2026: Critical PHP RCE Vulnerabilities Exploited (CVE-2026-109618, CVE-2026-109619); Fortinet AI-Driven Security Hardening Release for FortiOS and More
- PHP2Shell: What to know about two critical PHP flaws
- Discover and remediate PHP2Shell exposure with Tenable
- Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)
- Siemens Building Automation and Energy Products
- SANS Stormcast Monday, November 16th, 2026: Macfinger ClickFix DownTheDRAIN; Microsoft 365 Outage Phishing; Check Point PHP2Shell Exploits (CVE-2026-109618); Cursor Claude Code Extension